GDPR cookie consent requirements explained
Valid GDPR cookie consent comes before non-essential cookies load, via a clear action, with an equal reject option, easy withdrawal, and proof. Here's the checklist.
Valid GDPR cookie consent comes before non-essential cookies load, via a clear action, with an equal reject option, easy withdrawal, and proof. Here's the checklist.
GDPR cookie consent involves more than displaying a banner. Your website must block non-essential cookies until visitors consent, respect their choices, and keep records of that consent.
Use this 10-point checklist to understand the requirements and test how cookie consent works on your website.
Requirement | What it means | How to check |
|---|---|---|
| Tracking waits until the visitor consents | Visit your website without accepting cookies and see what loads |
| Only cookies needed for the service the visitor asked for skip consent | Compare each cookie's real function with its category |
| Visitors must actively consent | Check that optional categories start disabled |
| Refusing is as easy as accepting | Compare your Accept and Reject options |
| Purposes, third parties and duration are clear before the choice | Read your banner as a first-time visitor |
| Visitors can accept some categories and refuse others | Accept one category, reject another, and test the result |
| Refusing does not lock visitors out | Reject all and use the website normally |
| Visitors can change their minds at any time | Withdraw consent and check what stops |
| You can prove who consented, when and to what | Pull the record for a test visit |
| Choices are stored and refreshed when things change | Revisit your website and see whether your choice was kept |
GDPR cookie consent means getting a visitor's permission before using non-essential cookies or similar tracking technologies.
The ePrivacy Directive sets out when consent is required, while the GDPR defines what makes consent valid: it must be freely given, specific, informed, and unambiguous.
These rules also apply to technologies such as tracking pixels and local storage, not just traditional cookies, as the EDPB confirmed in Guidelines 2/2023.
Often, yes. Cookies that identify or track individual visitors can contain personal data under the GDPR.
However, cookie consent rules apply whether the information is personal data. Under the EU's Planet49 ruling, storing or accessing information on someone's device generally requires consent unless an exemption applies.
Most non-essential cookies require consent before they can be used. This includes advertising, analytics and other tracking technologies that are not necessary to provide a service the visitor requested.
Strictly necessary cookies, such as those used for shopping carts, login sessions, and essential security functions, generally don't require consent.
Some exceptions apply, particularly in the UK for certain analytics cookies and under specific national guidance, such as France's exemption for some audience measurement tools.
Legal requirement: ePrivacy Directive Art. 5(3), through national law
Consent has to come first. If your analytics or advertising tags fire on page load and the banner appears afterward, a later "Accept" cannot fix what already happened.
This is not a theoretical risk. In September 2025, the CNIL fined Shein €150 million, partly because it placed advertising cookies as soon as visitors landed on the website, before they could respond to the banner.
How to check it: Open your website in a private window, do not touch the banner, and look at what has loaded. Clym's free Pulse Chrome extension lists the third-party services on the page and labels each one Active or Blocked. It works with any consent management platform (CMP), not only Clym.
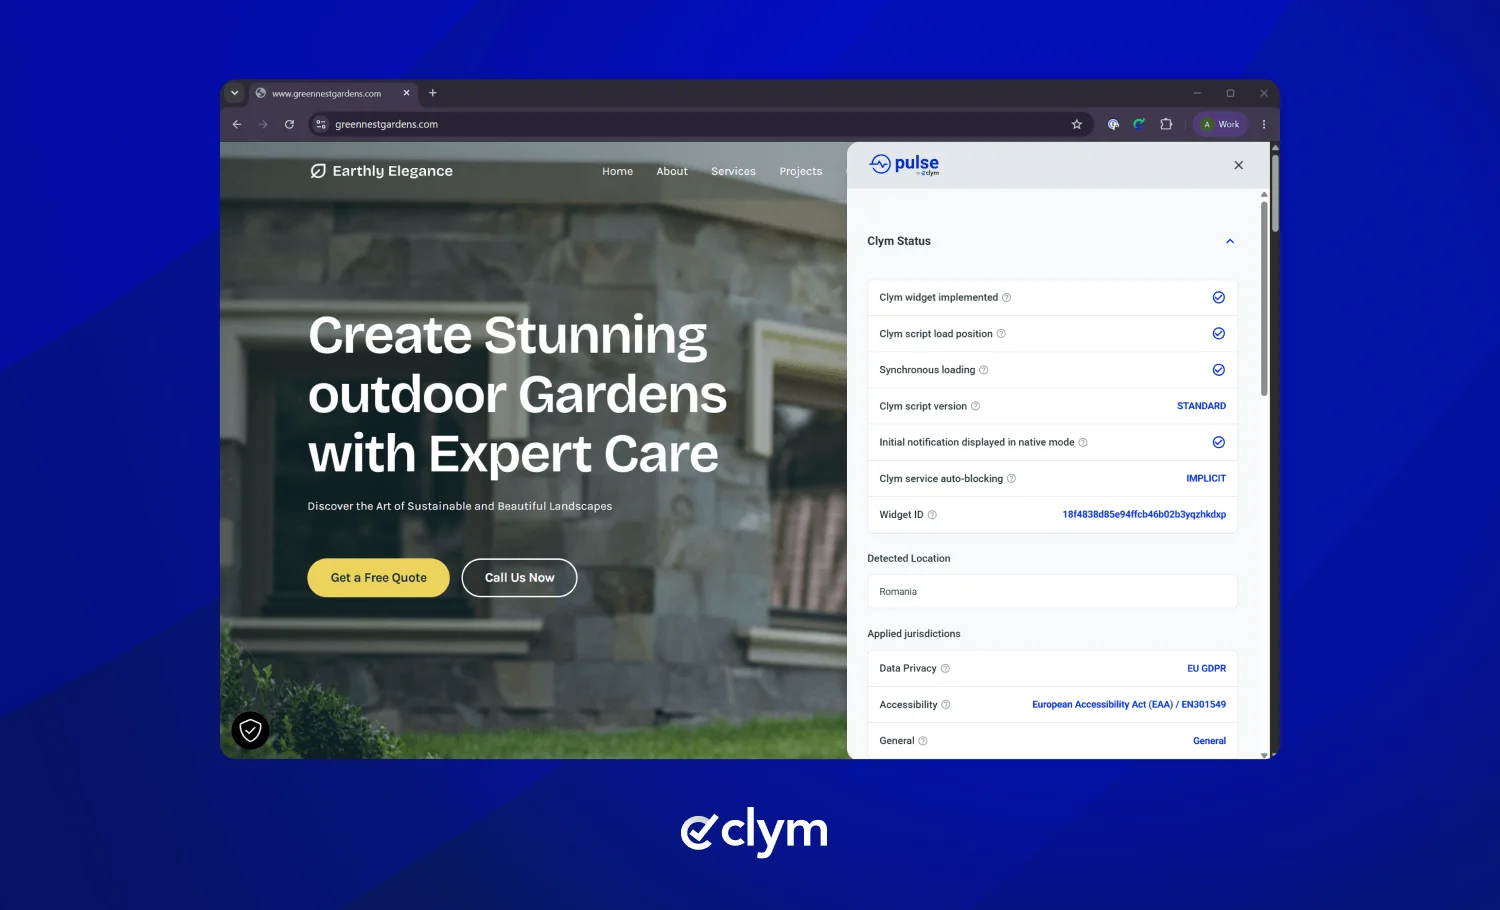
Legal requirement: the exemption in ePrivacy Directive Art. 5(3), as interpreted in [Article 29 Working Party Opinion 04/2012]
A cookie is not strictly necessary just because it is useful to your business. Only cookies needed to provide a service the visitor requested qualify for this exemption.
How to check it: List every cookie and tracker your website sets, then compare each one's actual function with its category. Clym's RealtimeCompliance™ recognizes more than 1,200 third-party services and classifies cookies by purpose and provider, which makes miscategorized cookies easier to spot.
Legal requirement: GDPR Art. 4(11) and Recital 32; CJEU, Planet49; [EDPB Guidelines 05/2020]
Consent requires a clear, affirmative action. Pre-ticked boxes, silence, scrolling, or simply continuing to browse do not count, as confirmed by EDPB guidance and the Planet49 ruling.
How to check it: Open your consent management widget on your website. Every non-essential category should start switched off. Then scroll, click a link, and move to a second page without touching the banner. Nothing non-essential should load.
Regulator expectation: [EDPB Cookie Banner Taskforce report] (January 2023) and CNIL guidance, based on GDPR Art. 4(11) and Art. 7
Visitors should be able to reject non-essential cookies as easily as they accept them. Hiding the Reject option behind additional clicks or making it less visible can undermine valid consent.
Regulators have taken action against these practices, including in the CNIL's €325 million Google case in September 2025.
How to check it: Compare your banner's Accept and Reject options. Both should be easy to find and use without unnecessary steps. For layout and wording, see our guide to cookie banner requirements.
Legal requirement: ePrivacy Directive Art. 5(3); GDPR Art. 13; CJEU, Planet49
Before visitors consent, they need to understand why you use cookies, which third parties receive their data, and how long the cookies last. A vague statement like "We use cookies to improve your experience" isn't enough.
You do not need every detail on the first layer. A short summary with a link to your cookie policy is standard. See our guide to what a GDPR cookie policy should include.
How to check it: Read your banner as a first-time visitor would. Can you tell that advertising cookies are used, and who receives the data? Then check that your cookie policy lists the cookies your website sets today.
Legal requirement: GDPR Art. 4(11) ("specific") and Recital 32
Consent must be specific to each purpose. Visitors should be able to accept analytics and refuse advertising, rather than face an all-or-nothing choice. Our article on granular consent explains how detailed those choices need to be.
How to check it: Accept one category and reject another, then confirm that only the accepted category's services load. With Clym Pulse open, you can watch services move between Blocked and Active as you change your choices.
Regulator expectation: GDPR Art. 7(4) and Recital 42; EDPB Guidelines 05/2020
Visitors generally should not have to accept non-essential cookies to access your website. Requiring consent as a condition of access can undermine whether that consent is freely given.
Some consent-or-pay models may be assessed differently. See our guide to cookie walls and consent-or-pay for more detail.
How to check it: Reject all, then use the website normally. Content and core features should still work.
Legal requirement: GDPR Art. 7(3)
Visitors must be able to withdraw consent as easily as they give it. A visible cookie settings link or icon should let them reopen their preferences and change their choices at any time.
How to check it: Withdraw consent and reload your website. Previously accepted tracking services should stop operating.
Legal requirement: GDPR Art. 7(1) and the accountability principle in Art. 5(2)
If a regulator asks, you need to show when a visitor consented, what they agreed to, and what information they saw.
A useful consent record includes a timestamp, the visitor's choices, and the version of the banner or policy displayed. A pseudonymous identifier can link the record to a specific choice. Keep records of refusals, too.
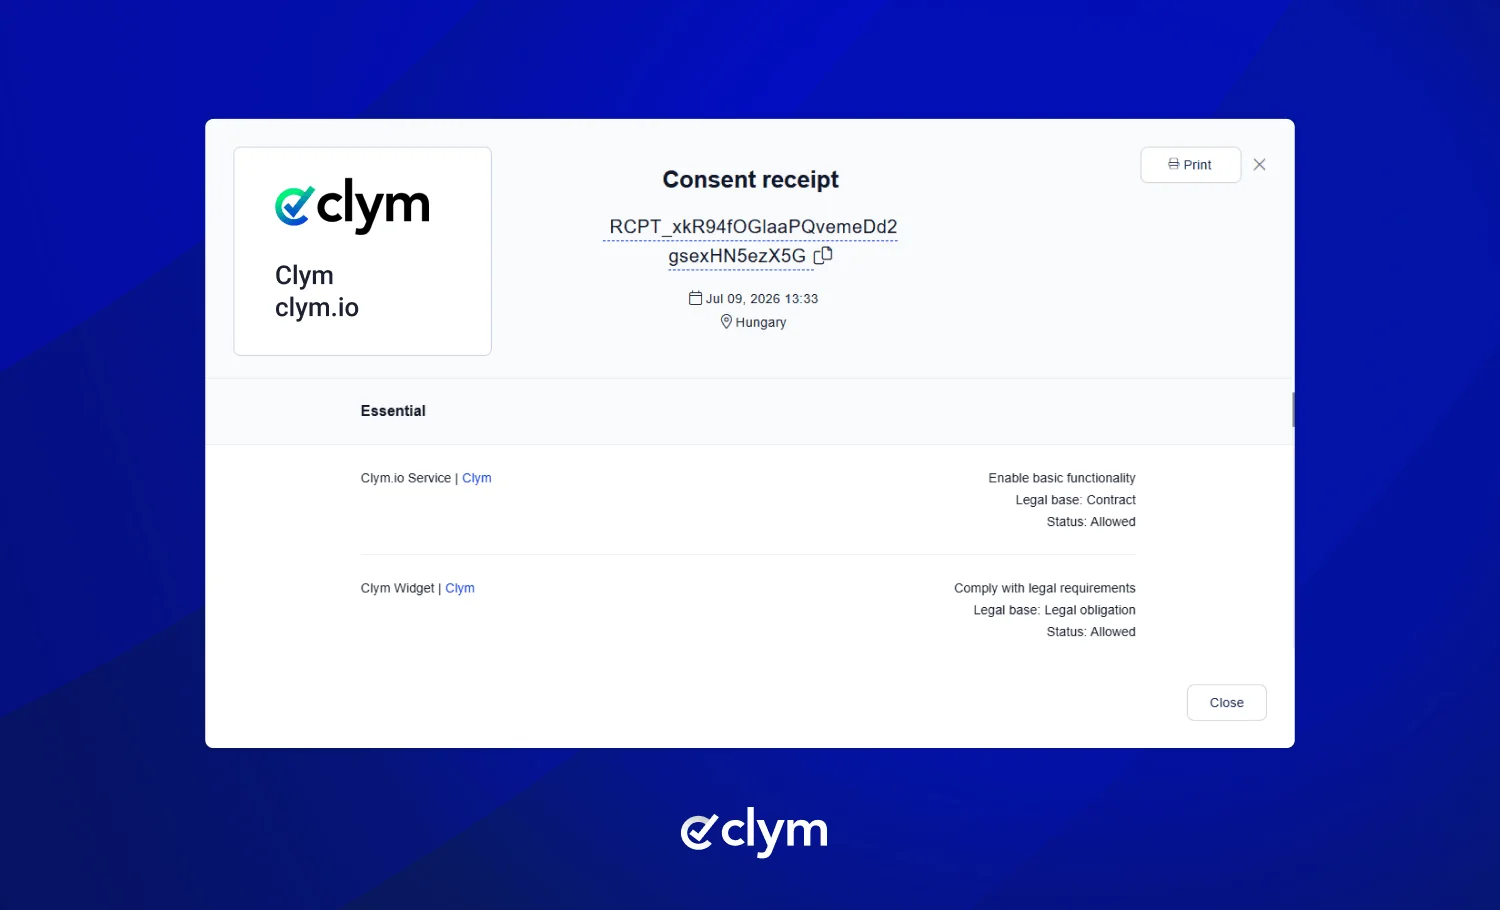
How to check it: Ask whoever manages your CMP to pull the consent record for a test visit. If nobody can, that is a gap.
Best practice: CNIL guidance (2020); EDPB Guidelines 05/2020
The GDPR does not set an expiry date for consent. Store each visitor's choice so the banner does not reappear on every page, and ask again when something material changes, such as a new purpose or a new third party. The CNIL considers keeping a choice for six months before asking again to be good practice.
How to check it: Make a cookie choice and revisit your website later. Your preference should be remembered. Also check whether visitors are asked for fresh consent when purposes or relevant third parties change.
Our GDPR cookie consent checklist explains each requirement and how to test it on your own site.
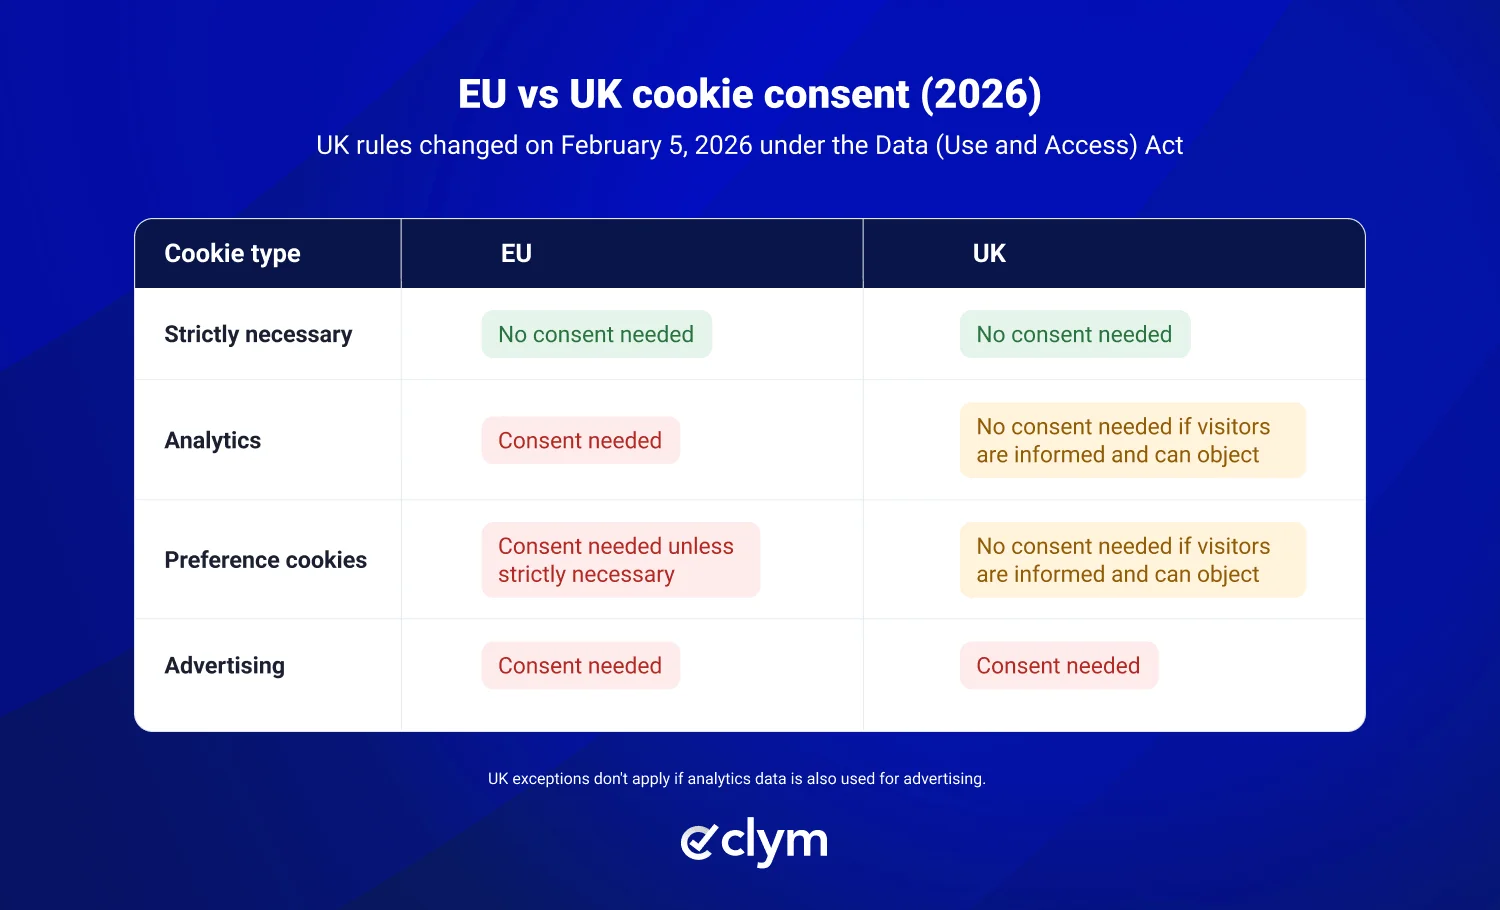
Most of this checklist also applies in the UK under the Privacy and Electronic Communications Regulations (PECR). Since February 5, 2026, however, the Data (Use and Access) Act 2025 lets UK sites use some analytics and preference cookies without consent.
These exceptions have conditions. You must provide clear information, offer a simple, free way to object, and stop when someone objects. Analytics that also feed advertising do not qualify, and advertising cookies still need consent, as the ICO's April 2026 guidance confirms. The Act also raised maximum PECR fines to £17.5 million or 4% of worldwide annual turnover.
The practical implication: a website serving both markets needs different behavior by location. Our article on the Data (Use and Access) Act and UK cookie consent covers the details.
Upcoming EU changes: The EU's Digital Omnibus proposal could change how cookie consent is handled. However, the proposal is not law yet, so the current requirements still apply.
Google Consent Mode communicates visitors' consent choices to Google services. It does not replace GDPR consent requirements, but it helps Google tags respond to those choices.
If you use Google Ads or analytics tools, check that your consent signals reflect what visitors actually selected. Pulse shows whether Consent Mode signals change when a visitor changes their choice. For setup instructions, see our guide to Google Consent Mode v2.
Clym helps businesses manage cookie consent, control tracking technologies, and test how consent choices work on their websites.
Cookie detection and blocking: RealtimeCompliance™ identifies more than 1,200 third-party services and helps prevent non-essential trackers from loading before consent.
Location-based rules: ReadyCompliance® provides adjustable default settings for more than 190 regulations based on each visitor's location.
Consent records: Stores a consent receipt for each visitor choice.
Free testing: Pulse shows what loads before and after consent on any page.
GDPR cookie consent goes beyond displaying a banner. Your website must block non-essential tracking before consent, respect visitors' choices, and keep records demonstrating valid consent.
Use this checklist to review your website regularly, especially when you add new cookies or tracking technologies.
This article is for general information and is not legal advice. For advice on your specific situation, consult a qualified privacy lawyer.
Yes, for non-essential cookies on a website used by people in the EU. You don't need consent for strictly necessary cookies, but you still have to tell visitors about them.
In the EU, generally yes. In the UK, since February 5, 2026, analytics used only to improve your own website can run without consent if you inform visitors and let them object.
The GDPR sets no fixed period. Store each choice, and ask again when your purposes or third parties change. The CNIL treats six months as good practice.
Yes, GDPR can apply to US companies that offer goods or services to people in the EU or monitor their behavior there (GDPR Art. 3(2)). This can include website tracking activities, even if the company has no office in the EU.
Cookie consent violations can result in significant fines under national ePrivacy laws. Where GDPR provisions are also violated, penalties for the most serious infringements can reach €20 million or 4% of worldwide annual turnover, whichever is higher.
Compliance Content Manager | CIPP/E (IAPP) | CPACC (IAAP)
Alex is a Compliance Content Manager at Clym, where he researches and writes about everything related to data privacy and web accessibility compliance for businesses, helping them stay informed on their compliance needs and spreading awareness about making the web safer and more inclusive. When he's not writing about compliance, Alex has his nose in a book or is hiking in the great outdoors.